AI /
The European Union embraces the era of artificial intelligence with the AI Act
EU AI Act: Operational Guide to the 2025–2028 Deadlines. Risk Mapping, Provider and Deployer Obligations, and Business Compliance Steps.

Smart Shaped
The EU AI Act (Regulation (EU) 2024/1689) is the world's first horizontal law governing artificial intelligence systems based on risk. It imposes distinct obligations on providers and deployers, with progressive deadlines between 2025 and 2028. Compliance requires an inventory of use cases, classification, governance, transparency, and operational controls.
What the AI Act is and why it changes how AI is developed and used in Europe
The AI Act (Regulation (EU) 2024/1689) is the European Union framework regulating the development, placement on the market, and use of AI Act (artificial intelligence systems) through a risk-based approach. Unlike a directive, a regulation is directly applicable in all EU Member States without requiring national transposition.
Its scope involves the European Commission, European Parliament, and Council of the European Union as the institutional architects of the law, but primarily targets operational roles: providers (those who develop or market systems), deployers (those who use systems), importers, and distributors. The AI Act also features extraterritorial reach: it applies to systems affecting individuals or the market within the EU, even if developed outside its borders.
Three core goals drive this architecture: safety, protection of fundamental rights (privacy and non-discrimination), and innovation (competitiveness and trust). Market adoption is accelerating rapidly: in 2025, 20.0% of EU enterprises with at least 10 employees reported using AI technologies (Eurostat, published 2025-12-11). Eurostat Source.
How the risk-based approach of the AI Act works
The AI Act does not ban AI outright: it categorizes use cases into four risk tiers and assigns proportionate obligations. Risk classification is the crucial step enabling procurement, governance, and auditing—without a clear risk-to-use-case map, boards and compliance teams cannot define controls, vendor SLAs, or production readiness criteria.
| AI Act Category | Typical Examples | Key Obligations | Business Impact |
|---|---|---|---|
| Prohibited Practices | Manipulation, social scoring | Total prohibition | Immediate halt, system removal |
| High Risk (Annex III) | HR, healthcare, transport | Risk mgmt, logging, oversight | Audits, QMS, vendor due diligence |
| Limited Risk (Transparency) | Chatbots, deepfakes | User disclosures | UX updates, policies, content labeling |
| Minimal Risk | Spam filters, video games | Few obligations | Good practices and monitoring |
Two frequently cited examples of prohibited practices include deceptive manipulation and indiscriminate social scoring. The "high risk" tier (detailed in Annex III) covers areas such as employee recruitment, access to essential services, and safety-critical applications. For systems posing "limited risk," transparency rules apply to chatbots and deepfakes. For an in-depth look at model-related technical risks relevant to classification, see managing model collapse risks when deploying AI foundation models.
Which systems and sectors are most affected by the AI Act
The impact of the AI Act depends on the risk level of the specific use case, rather than the industry alone. A single enterprise might deploy minimal-risk systems (internal automation) alongside high-risk applications (decisions impacting individual rights, service access, or safety). This nuance shapes how teams design technical requirements, testing, procurement, and operational governance.
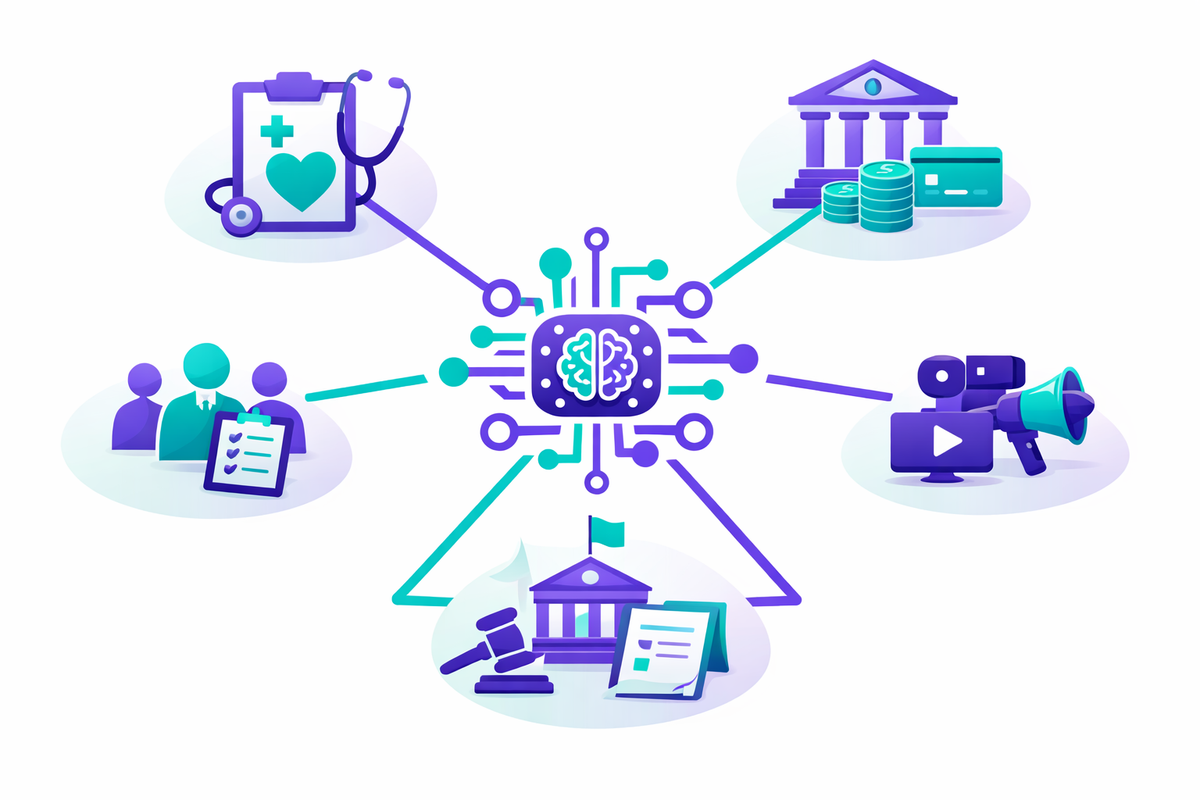
Healthcare: computer-aided diagnostic, triage, and clinical decision support systems typically require rigorous governance, full auditability, and human oversight. Financial Services: credit scoring and fraud detection models may fall into high-risk categories, carrying major implications for audit trails, non-discrimination controls, and quality management. Human Resources: automated recruiting, CV screening, and performance evaluation tools demand strict attention to bias mitigation and explainability.
Public Administration and migration management: sensitive deployment scenarios require enhanced scrutiny, accountability, and strict necessity and proportionality criteria. Media and Marketing: transparency expectations are rising around synthetic content and deepfakes. For practical examples of sectoral traceability using advanced digital architectures, see leveraging digital twins for AI regulatory compliance traceability. For SMEs, compliance costs can be mitigated through regulatory sandboxes and targeted public support.
What changes for foundation models and GPAI under the AI Act
A foundation model (a base model trained on vast datasets to be fine-tuned across diverse downstream tasks) and a GPAI model (General-Purpose AI, capable of performing a wide range of distinct tasks) introduce novel regulatory obligations, as risks depend not only on the end application but also on the underlying model characteristics.
There is a significant difference between developing a model (training, dataset curation, evaluation) and integrating one via cloud APIs: many European businesses leverage third-party models (such as those from OpenAI, Anthropic, Google, or Meta) for enterprise chatbots, copilots, search assistance, and document generation. Even without training the model, the enterprise remains responsible as a deployer for its configuration, usage, transparency, data governance, and oversight.
Early legislative debates included requests (led by Italy, France, and Germany) to exempt foundation models from direct regulation; however, the final text established targeted obligations—particularly for high-impact models with systemic risks—around technical documentation, copyright transparency, and systemic risk management. The European Commission published dedicated guidelines for GPAI providers: Guidelines for providers of general-purpose AI models. For market insights on frontier models, see AI regulation and market impacts on AI foundation models.
AI Act Timeline: key deadlines from 2025 to 2028
The implementation timeline is phased: certain prohibitions and general-purpose rules apply early, while others (such as transparency and high-risk requirements) take effect later. This phased rollout requires enterprises and providers to structure compliance in waves: procurement and legal teams address prohibited practices and vendor contracts immediately; product and IT teams build logging, testing, and disclosure interfaces; while compliance leads set up training and audit structures.
| Date | Category / Actor | Provisions Entering into Force | Practical Impact |
|---|---|---|---|
| 2 Aug 2025 | GPAI Providers | General-Purpose AI obligations apply | Policies, technical docs, risk mgmt |
| 2026 (2 Aug) | Transparency (Art. 50) | Chatbot/deepfake disclosure rules | UX labeling, disclosure workflows |
| 2027 | Pre-existing GPAI | Deferred deadline for legacy systems | Updating contracts and compliance proof |
| 2028 | High-Risk Systems | Full application for Annex III uses | QMS, conformity audits, human oversight |
The European Commission explicitly clarifies that for GPAI providers: “These obligations entered into application on 2 August 2025.” (European Commission guidance, source). Regarding transparency obligations, official guidelines state that Article 50 applies from August 2, 2026: Transparency obligations for AI providers and deployers. To read more on upcoming deadlines, see key deadlines and upcoming obligations under the EU AI Act.
How to align with the AI Act: an operational checklist for enterprises, providers, and deployers
Achieving compliance with the AI Act requires governance structures, use case inventories, risk classification, technical documentation, and staff literacy. In real-world digital transformation projects led by Smart Shaped S.r.l. since 2015, the most common bottlenecks are not purely technical: they center on vendor mapping, use case ownership, and generating verifiable audit evidence.
- AI Inventory: audit and map all AI systems, datasets, prompts, integrations, and external vendors (procurement + IT + product owners).
- Classification: map each use case to Prohibited / High-Risk / Transparency / Minimal risk categories (legal + compliance).
- Roles & Governance: define formal responsibilities across the board, compliance officer, DPO (Data Protection Officer), and product leads.
- Gap Analysis: evaluate technical requirements (logging, quality assurance, human oversight) against operational processes (policy, incident response).
- Documentation: build audit trails, system registries, testing evidence, and update vendor procurement contracts.
- AI Literacy: train internal users and risk functions, establishing clear usage policies and content guidelines.
- Continuous Monitoring: track performance metrics, conduct periodic reviews, and adapt to secondary EU implementing acts.
For a comprehensive operational playbook, see managing AI governance and EU AI Act compliance in enterprise environments. For small business perspectives, read AI adoption in SMEs and practical tools for operational readiness.
Penalties, enforcement, and regulatory sandboxes: risks and opportunities
The AI Act balances substantial fines with legal mechanisms designed for controlled innovation. Operationally, enforcement is not merely about financial penalties: it entails inspections, official document requests, control verifications, and the legal burden of demonstrating that an AI system was built and monitored with risk-proportionate measures.
Regulatory oversight involves national competent authorities coordinated at the EU level by the newly established AI Office. For enterprise teams, this requires maintaining an unambiguous chain of documentation connecting vendors, business line managers, and compliance functions.
Regulatory sandboxes (supervised testing environments with adapted regulatory requirements) offer a pathway to accelerate high-stakes projects. Realistic examples include: (1) Healthcare, controlled clinical validation of an AI triage assistant under protocol supervision; (2) Fintech, testing fraud detection models using pseudonymized datasets with active bias monitoring; (3) Public Administration, trialing document automation with complete audit logging. According to a joint OECD-EC report published in 2025, roughly two-thirds of EU Member States have launched dedicated initiatives to support AI adoption, particularly among SMEs (published 2025-11-24 on Futurium).
AI Act vs. global regulations: what makes the European framework unique
The EU approach stands out because it is horizontal (applying across industries), risk-based, and holds extraterritorial power. This forces global tech vendors and cloud providers to harmonize upwards, elevating baseline security and transparency controls worldwide to remain compliant within the European single market. A clear indicator of industry commitment is market participation in voluntary standards: enterprise commitments under the EU AI Pact.
In the United States, AI regulation remains decentralized and sector-specific; frameworks like the NIST AI RMF (AI Risk Management Framework) provide risk management guidelines but lack binding legislative authority. In the United Kingdom, regulators favor a principle-based, sector-led strategy with tailored guidance.
For corporate governance, it is essential to distinguish between binding laws and voluntary management standards: ISO/IEC 42001 (the international management system standard for AI) provides an operational structure for risk management and continuous improvement, but does not replace statutory EU legal mandates. Globally, the European Commission collaborates with the OECD to track national strategies and AI infrastructure investments: European Commission/OECD official source.
Article 50 of the AI Act applies from 2 August 2026. It sets out transparency obligations for providers and deployers of certain AI systems, including generative and interactive AI systems and deepfakes.
— European Commission, Official guidance on transparency obligations
EU AI Act FAQ for Businesses
How widespread is AI adoption among EU businesses and why does it matter for compliance?
In 2025, 20.0% of EU enterprises with at least 10 employees used AI technologies, up from 13.5% in 2024 (Eurostat, published 2025-12-11). This makes compliance a mainstream business priority: more production use cases mean a greater need for system inventories, risk classification, and auditable governance.
If I use a third-party AI model via API (e.g., ChatGPT), do I still have compliance obligations?
Yes: an enterprise integrating a third-party model incurs obligations as a deployer, particularly regarding user transparency disclosures, internal governance, and use-case risk management. The fact that model training and core technical documentation belong to the upstream provider does not eliminate liability for enterprise configuration, data handling, output validation, and human supervision.
What is the difference between "high risk" and "transparency" under the AI Act?
High-risk systems (Annex III) require extensive controls, including continuous risk management, logging, quality management systems (QMS), and human oversight. Transparency obligations (Art. 50) specifically mandate clear disclosures for chatbots, synthetic content, and deepfakes, ensuring end users know when they are interacting with or viewing AI-generated content.
What is a regulatory sandbox and how does it help SMEs?
A regulatory sandbox is a supervised testing framework that allows businesses to experiment with AI systems under controlled conditions with tailored regulatory guidance. For SMEs, sandboxes reduce validation costs and development timelines, provide access to data and partners, and build verifiable proof of safety before commercial deployment.
Who should be involved internally to build an effective AI Act compliance team?
Compliance requires a cross-functional team: executive leadership and the board for resource allocation, legal and compliance for risk mapping and audits, the DPO for data protection alignment, procurement for vendor contracting and due diligence, IT and AI leads for technical logging and security, and product owners to translate compliance requirements into user experience and operational workflows.