AI /
AI Regulation: Why Big Tech Asks for Rules but Rejects the EU AI Act
Big Tech and AI Rules: Why Silicon Valley Giants Demand Guardrails in the US but Reject the EU AI Act? Smart Shaped's Analysis.

Smart Shaped
Last update: September 15, 2026
Big Tech companies call for "global" Artificial Intelligence rules, yet resist the EU AI Act because the European regulation converts abstract principles into binding obligations: risk classification, technical transparency, mandatory audits, legal liability, and enforceable penalties. In short, endorsing shared guardrails is no longer enough: in the EU, compliance becomes immediate, measurable, and punishable.
The public debate surrounding Artificial Intelligence is undergoing a dramatic shift: moving past job displacement concerns, data center water and energy consumption, and model hallucinations, focus is rapidly shifting toward systemic safety and alignment. Warnings issued by Dario Amodei (CEO of Anthropic) - echoed by key figures such as Sam Altman and Elon Musk - concerning the catastrophic risks of autonomous AI agents and frontier models have reignited this conversation. Concurrently, global markets and major industry players (ranging from NVIDIA to SoftBank) react sharply to every signal of potential regulatory tightening.
What is the EU AI Act and why is it at the center of the clash with Big Tech?
The EU AI Act (Regulation EU 2024/1689) is the world's first horizontal law regulating AI through a risk-based approach, imposing tailored obligations across distinct risk tiers. It sits at the absolute epicenter of the conflict because it transitions governance from voluntary ethics to mandatory legal compliance backed by public oversight, audits, and statutory fines. The European Commission summarizes this core foundation as follows:
At the core of the EU AI Act is a proportionate, risk-based approach that tailors regulatory obligations based on the level of risk an AI system poses to health, safety, and fundamental rights.
— European Commission, Directorate‑General for Communications Networks, Content and Technology
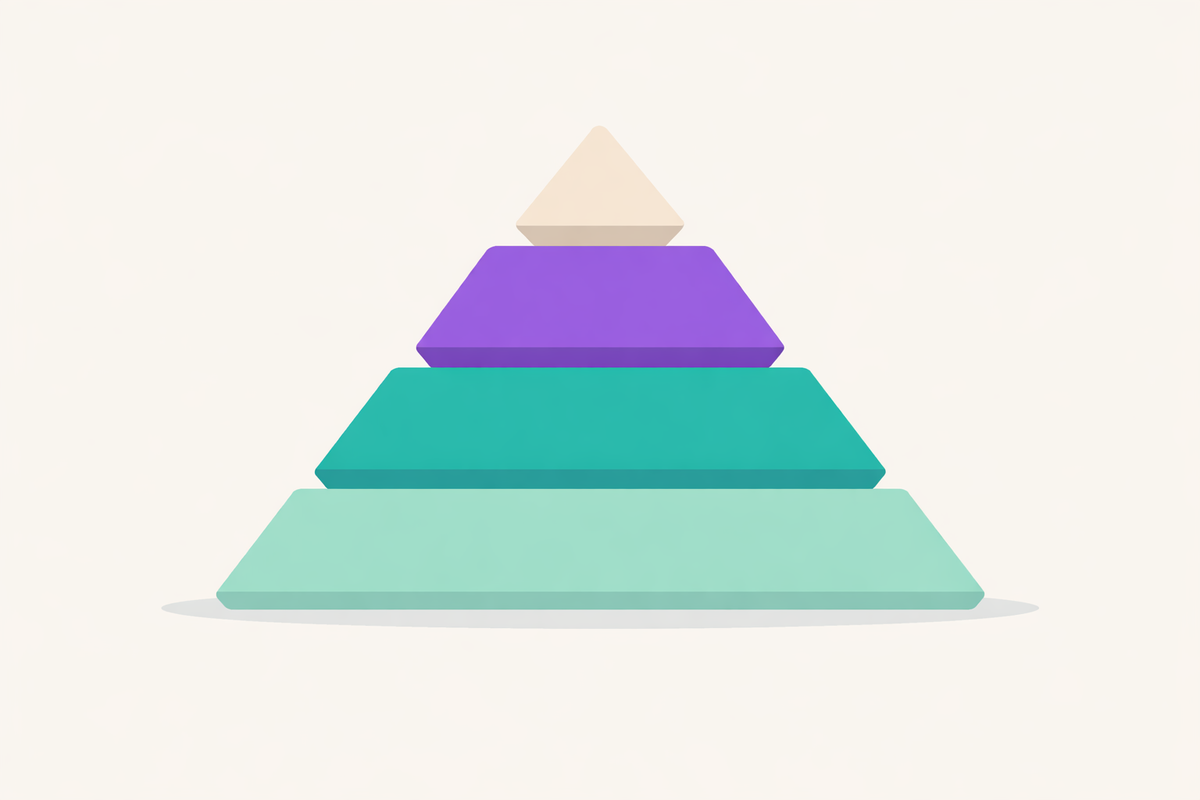
The regulation strictly categorizes prohibited practices, high-risk systems, transparency mandates, and rules for general-purpose AI models (GPAI / foundation models). Supervisory authority over GPAI falls under the newly formed AI Office (the EU coordination and enforcement body). Operational timelines are explicitly detailed across EU sources and 2026 regulatory updates: bans on prohibited practices take effect from February 2, 2025 (Cyvra, 2026), GPAI provider rules apply starting August 2, 2025, and full enforcement kicks in on August 2, 2026 (Software Improvement Group, August 2026 update).
| AI Act Category | Examples | Typical Obligations | Application Phase |
|---|---|---|---|
| Unacceptable Risk (Prohibited) | Public social scoring; real-time biometric identification (with strict exceptions) | Complete ban + severe penalties | From Feb 2, 2025 |
| High Risk (Annex III) | HR & recruitment; credit scoring; healthcare; critical infrastructure | Risk management, detailed logging, data quality, human oversight | From Dec 2, 2027 (Inside Privacy, 2026) |
| Transparency Risk | Chatbots; deepfake content generation | User disclosure, clear AI labeling | Progressive 2025–2026 |
| GPAI / Foundation Models | General-purpose generative AI foundation models | Technical documentation, transparency summaries, copyright policy compliance | From Aug 2, 2025; full enforcement Aug 2, 2026 |
For broader regulatory context, read our in-depth analysis on the impact and operational compliance steps of the EU AI Act in Europe.
Why do Big Tech companies ask for global rules while contesting European ones?
Big Tech firms enthusiastically support rules in abstract terms but resist immediately enforceable and punitive measures: the dispute is not about "whether" to govern AI, but who gets to define standards, control audits, and assign liability. In the United States, public corporate statements emphasizing safety and independent audits (from Anthropic to OpenAI) coexist with intense lobbying that views these calls as potential "Trojan horses" designed to entrench incumbents against open-source rivals and emerging startups.

This "dual narrative" is visible in the stark divide between public relations rhetoric and actual policy demands: slowing down the race to ever-more extreme models can help curb skyrocketing infrastructure costs and lock in ROI on already mature enterprise use cases (RAG, document automation, business analytics). In the EU, however, that same governance requires ex-ante verification, data lineage, and legal accountability.
| Perspective | Public Statement | Operational Demands (Policy / Lobbying) |
|---|---|---|
| Safety | Universal safety benchmarks and independent audits | Voluntary codes of practice, interpretive flexibility, enforcement delays |
| Competition | Mitigating risks of autonomous agents and frontier models | Negotiable rules, reliance on ex-post enforcement |
| Markets | Framing global governance as a public good | Gradual, phased compliance to minimize immediate operational expenses |
In Europe, the single market functions as the premier regulatory arena where de facto global tech standards are set. A related analysis on tech leadership dynamics is available in our piece on AI regulation and how tech giants rewrite the rules of the game.
Which specific provisions of the EU AI Act are Big Tech companies truly contesting?
Recurring objections from Big Tech center on four critical areas: compliance overhead, legal uncertainty during guideline rollout, structural overlap with GDPR (General Data Protection Regulation), and strict requirements for GPAI / foundation models (base models trained on vast datasets for downstream adaptation). Concurrently, firms challenge the aggressive enforcement timelines alongside the operational readiness of official registries and EU guidance.

The resistance extends beyond political rhetoric: while some criticisms reflect genuine operational friction (technical clarity, harmonizing with GDPR data processing rules), others function as tactical negotiations aimed at delaying enforcement. The voluntary AI Pact (an EU initiative for early commitment) is frequently highlighted by vendors as a flexible alternative, though it lacks the force of law.
| Big Tech Objection | Regulatory Friction Point | Validity of Claim | EU Framework Reality |
|---|---|---|---|
| "Excessive Bureaucracy" | Mandatory documentation and audit logging | Partially valid | Risk-proportionate obligations (European Commission) |
| "Uncertainty around GPAI" | Transparency summaries & copyright compliance | Valid during guideline drafting phase | Rules active since Aug 2, 2025 (SIG, 2026) |
| "Overlap with GDPR" | Training data legality and legal bases | Valid in specific implementation cases | AI Act + GDPR co-exist on complementary regulatory layers |
| "Unrealistic Timelines" | High-risk Annex III / Annex I deadlines | Significantly valid | Enforcement deferred to 2027–2028 (Inside Privacy, 2026) |
For key details on voluntary enterprise commitments, explore the EU AI Pact signed by global tech leaders.
EU AI Act vs. United States: what regulatory differences explain the clash?
The fundamental distinction is structural: the EU selected a horizontal, binding legal framework (the EU AI Act), whereas the United States maintains a decentralized approach characterized by non-binding frameworks, sector-specific rules, and ex-post regulatory enforcement. For Big Tech, a negotiable, fragmented regime significantly lowers the risk of having to rapidly restructure core architectures to meet a rigid "hard law" standard in a major market.

| Dimension | EU (EU AI Act) | US (Prevalent Approach) | Big Tech Impact | Startup Impact |
|---|---|---|---|---|
| Structure | Single unified regulation | Fragmented and sector-specific | "One-shot" architectural compliance | Higher legal uncertainty, but fewer upfront mandates |
| Obligations | Ex-ante risk prevention | Primarily ex-post enforcement | Upfront compliance overhead | Varies significantly by industry sector |
| Penalties | Up to €35M or 7% of global turnover | Variable by agency/sector | Direct statutory legal liability in EU | Risk of potential EU market entry barriers |
For further analysis, see the regulatory comparison between the EU and US in the AI race and how US model policy shifts impact enterprise AI strategies.
Does a global AI governance framework exist, or just competing regulations?
Today, a unified global AI governance framework does not exist: instead, the market presents a complex mosaic of technical standards, voluntary agreements, and competing national regulations. While the EU, US, and China agree that foundation models carry profound systemic and safety risks, they diverge sharply on regulatory mechanisms (hard law vs. soft law) and core priorities (fundamental rights vs. commercial competitiveness vs. national security).

Prominent scientific figures such as Demis Hassabis (Google DeepMind) have called for independent international bodies capable of evaluating frontier models prior to public release, while enterprises like Microsoft continue to strengthen internal safety guardrails to maintain operational human oversight over AI agents. On the multilateral stage, efforts like the G7 Hiroshima AI Process and international frameworks such as the OECD AI Principles foster international interoperability, yet do not replace domestic statutory law.
- Points of Convergence: Risk evaluation methodologies, cybersecurity baselines, minimal data lineage, and frontier model safety checks.
- Points of Divergence: Enforcement mechanisms, training data transparency mandates, weight given to fundamental human rights, chip access, and supply chain controls.
Who is hit hardest by AI rules: startups, Big Tech, or enterprise deployers?
The burden of AI regulation is not distributed equally: Big Tech hyper-scalers can absorb legal compliance expenses, mandatory audits, and governance overhead; startups face fixed cost barriers and early-stage legal uncertainty; while enterprise deployers (banks, universities, healthcare systems) bear the brunt of procurement due diligence, use-case risk assessments, and human oversight requirements. In practice, mature compliance capabilities are turning into a key competitive advantage for well-capitalized organizations.
High-risk use cases under Annex III include AI applications in HR (automated hiring and screening), credit evaluation (credit scoring), and healthcare (clinical decision support). In these scenarios, the enterprise deployer must demonstrate strict operational controls, complete system logging, and a robust human-in-the-loop protocol. In enterprise deployments across regulated industries, moving from "pilot" to "production" relies entirely on generating verifiable, auditable evidence across the AI supply chain.
For small business perspectives, see AI adoption in SMEs and regulatory impacts.
How should enterprises prepare today for the EU AI Act?
Organizations should not wait for perfect regulatory guidelines before initiating AI governance: the EU AI Act turns readiness into a practical operational routine centered on inventory, classification, and continuous monitoring. A stark warning from the Cloud Security Alliance notes that as of 2026, "the majority of large European enterprises still lack a mature risk management framework specifically tailored to AI" (Cloud Security Alliance, 2026) - even as enforcement deadlines draw near.
A 5-step operational framework for regulated sectors (banking, healthcare, and higher education):
- Comprehensive Inventory of all internal AI systems (including shadow AI and embedded vendor tools).
- Risk Classification aligning each application with AI Act categories and internal risk policies.
- Vendor Due Diligence evaluating GPAI models, training data transparency, logging specs, and SLAs.
- Human-in-the-Loop Implementation across high-stakes decision points and escalation workflows.
- Continuous Audit Trails & Monitoring tracking model drift, data lineage, and incident response.
| Compliance Challenge | Business Risk | Practical Countermeasure |
|---|---|---|
| Mapping AI Use Cases | Shadow AI deployments & non-compliance | Centralized AI Registry + assigned process owners |
| Evaluating GPAI Vendors | Contractual liability & reputational damage | Vendor questionnaires + technical proof + log access |
| Human Oversight | Errors in credit, HR, or healthcare decisions | Mandatory decision checkpoints + approval workflows |
| Data Provenance | GDPR violations & copyright infringement | Data lineage tracking + data minimization policies |
For a comprehensive operational playbook, consult our complete guide to enterprise AI governance and compliance.
EU AI Act FAQ: Big Tech and Enterprise AI Compliance
When do the primary enforcement provisions of the EU AI Act take effect?
Bans on unacceptable risk practices became active on February 2, 2025. Obligations governing general-purpose AI (GPAI) models apply from August 2, 2025, with full GPAI sanction enforcement starting August 2, 2026. High-risk system compliance deadlines under Annex III defer to 2027–2028.
What are the financial risks of non-compliance with the EU AI Act?
Non-compliance carries costs far exceeding the investment required for governance programs. Penalties under the AI Act reach up to €35 million or 7% of total global annual turnover for prohibited practice violations, with tiered fines for other compliance failures.
What is the practical distinction between the EU AI Act and GDPR for business AI deployers?
GDPR governs personal data privacy and legal processing bases, whereas the EU AI Act regulates AI system risk, technical performance, and mandatory controls (such as logging, human oversight, and safety audits). Most enterprise deployments require compliance with both: GDPR for underlying personal data, and the AI Act for system risk, transparency, and vendor accountability.
Are European startups and SMEs disadvantaged by the EU AI Act compared to Big Tech?
Yes, primarily due to upfront fixed compliance expenses and initial regulatory ambiguity. While Big Tech firms easily absorb audit costs across global product portfolios, startups must invest early in documentation, legal reviews, and vendor due diligence. However, early compliance can serve as a distinct commercial trust asset within the European market.
What immediate steps should a CIO or Compliance Officer take in a bank or university?
The immediate priority is creating a comprehensive inventory of all active AI systems (including shadow AI), classifying use cases by risk tier, and establishing formal vendor due diligence for third-party GPAI integrations. Next, set up human-in-the-loop decision checkpoints and maintain minimal audit trails (system logging and incident response protocols) to reduce legal exposure and streamline procurement.